Strengthening Credit Union Cybersecurity Through Zero Trust and Continuous Monitoring
USMICRO established an ODC-led cybersecurity operating model that combined Zero Trust access controls, continuous threat monitoring, endpoint protection, incident-response readiness and vendor-risk discipline across critical credit-union technology environments.
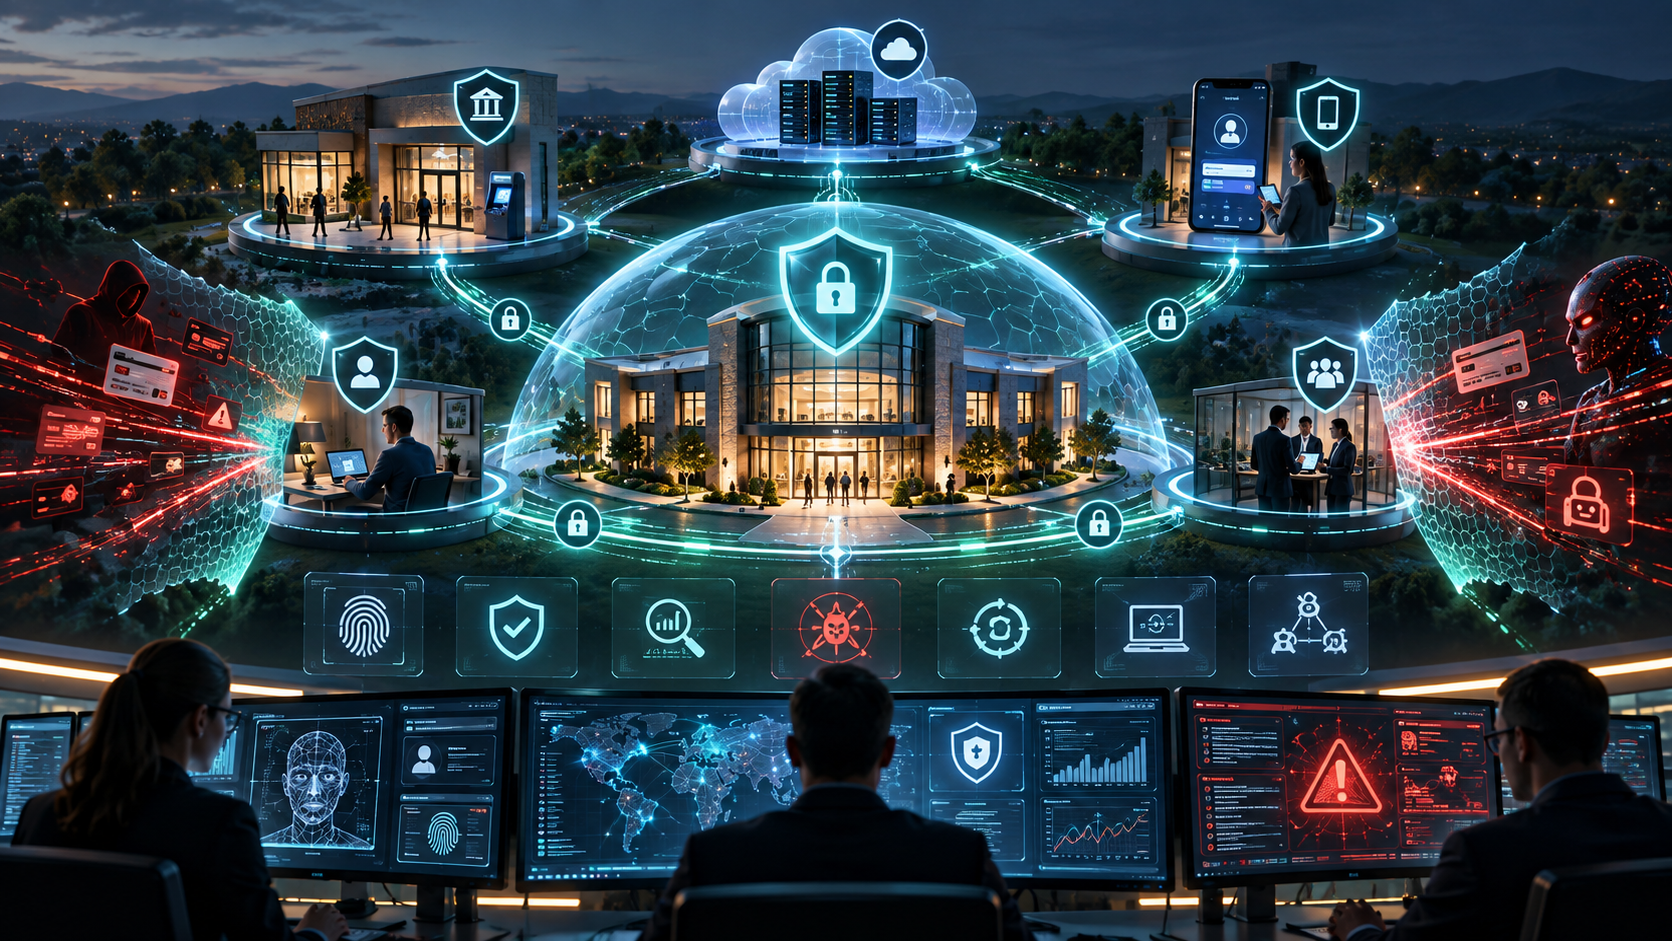
What needed to change.
The credit union was responsible for protecting sensitive financial and member information across digital banking, payment systems, branch environments, cloud services and remote-work endpoints while operating with comparatively lean internal security resources.
At the same time, the threat landscape was becoming more complex. Ransomware, compromised credentials, AI-enabled fraud, deepfake-assisted social engineering and vulnerabilities introduced through third-party vendors created multiple potential entry points into the institution.
A compromised user identity, endpoint or partner connection could become a pathway into broader systems if access controls and segmentation were insufficient.
Security visibility was also fragmented across identities, devices, applications and cloud environments, making it harder to detect suspicious activity early or correlate signals across systems.
Manual monitoring and inconsistent response procedures increased the risk that abnormal behavior could remain unnoticed until it created operational disruption.
The challenge was therefore not simply deploying more security tools. It was establishing a layered security model that improved identity assurance, reduced lateral-movement risk, strengthened detection and created a repeatable response and governance framework.
How the problem was approached.
USMICRO established a dedicated Offshore Development Center combining cybersecurity specialists, infrastructure engineers and risk-focused technical support.
The programme began by examining identity, endpoint, application, cloud and third-party access patterns to identify where controls, visibility and response processes required strengthening.
Zero Trust principles were introduced across critical access paths through stronger authentication, least-privilege permissions, continuous verification and segmentation.
The ODC team also integrated centralized monitoring across endpoints, identities and cloud environments so abnormal behavior could be detected and investigated through a more coherent operational view.
Endpoint-protection and response workflows were standardized to reduce dependence on purely manual intervention.
Incident-response procedures, escalation paths and tabletop exercises were formalized so security events could be handled through predefined actions rather than improvised coordination.
Third-party security reviews were incorporated into the operating model to address risk introduced through vendors and external technology dependencies.
What changed in the technology environment.
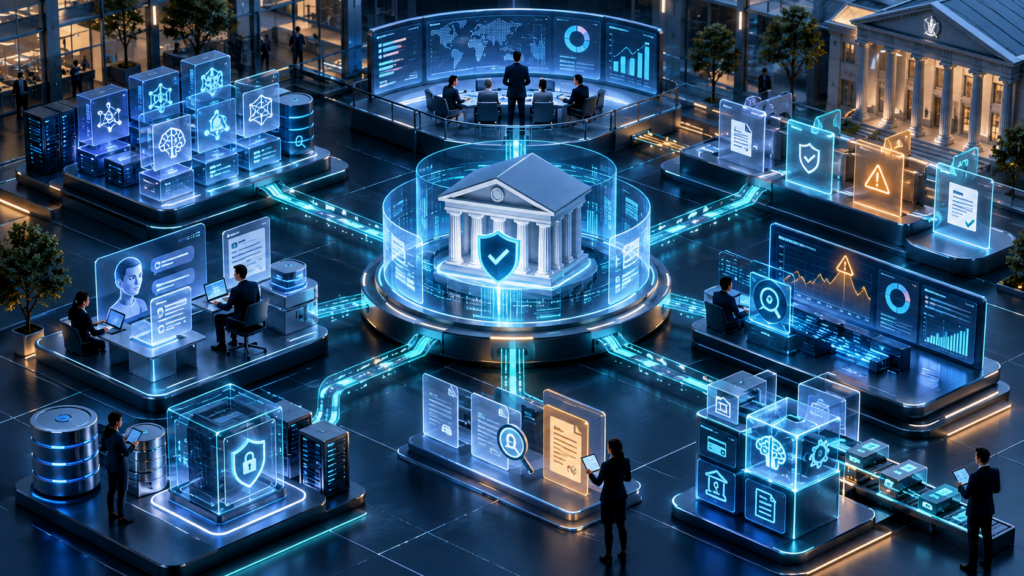
USMICRO introduced a layered cybersecurity architecture spanning identity, endpoint protection, monitoring, segmentation, incident response and vendor-risk controls.
Identity and Access Management controls enforced multi-factor authentication, least-privilege access and continuous identity verification across supported critical environments.
Network and application segmentation reduced unnecessary trust relationships and limited the ability of a compromised identity or device to move laterally across systems.
Endpoint Detection and Response capabilities provided visibility into suspicious processes, anomalous behavior and potential file-encryption activity across protected devices.
Centralized monitoring pipelines correlated signals from identities, endpoints and cloud environments to support earlier identification of events such as impossible-travel activity, abnormal access patterns and suspicious execution behavior.
Incident-response management introduced structured playbooks, escalation paths and evidence capture for priority security scenarios.
Third-party security assessment workflows strengthened visibility into vendor risk and created a more repeatable basis for reviewing external access and technology dependencies.
The architectural shift was therefore from fragmented security tools and manually coordinated response toward identity-centric controls, continuous monitoring, segmented access, structured incident response and governed third-party risk management.
What can be credibly demonstrated.
The new security operating model materially improved the credit union’s visibility and control across critical technology environments.
Stronger identity verification and least-privilege access reduced unnecessary trust relationships and created clearer boundaries around privileged and sensitive systems.
Continuous monitoring across endpoints, identities and cloud environments improved the institution’s ability to identify suspicious activity earlier and investigate events through a more centralized operational view.
Endpoint-protection and segmentation controls strengthened resilience against scenarios in which a compromised user or device could otherwise create broader disruption.
Formal incident-response playbooks and simulation exercises improved organizational readiness by giving technical and leadership teams defined escalation and response procedures.
Vendor-risk reviews also created a more systematic way to evaluate external technology dependencies rather than treating third-party security as a periodic administrative exercise.
The ODC model gave the credit union continuing cybersecurity engineering and operational capacity without requiring equivalent expansion of the internal security organization.