Scaling Banking AI Through a Governed Operating Model
USMICRO established an ODC-led AI governance environment that centralized model visibility, automated use-case approvals, introduced lifecycle controls and created continuous monitoring for models, copilots, assistants and automated decision systems.
What needed to change.
The bank had moved beyond isolated AI experimentation and was beginning to face the more difficult question of how artificial intelligence could be scaled safely across the enterprise.
AI use cases were expanding into areas including underwriting, automated credit decisioning, customer service, copilots and emerging agentic workflows.
As adoption increased, so did the risk surface. Potential issues included model bias, hallucination, drift, prompt manipulation, inappropriate tool access, data leakage and inconsistent decision traceability.
Informal experimentation and fragmented control policies made it difficult to maintain a reliable inventory of which models and assistants were operating, what data they used, how they had been validated and which controls applied to each use case.
This created both operational and governance risk. AI systems that performed well during experimentation still needed to remain explainable, monitored and defensible once they entered production.
The challenge was therefore not simply to accelerate AI adoption. It was to create an operating model in which innovation could scale without weakening accountability, control discipline or auditability.
How the problem was approached.
USMICRO established a dedicated Offshore Development Center combining AI governance specialists, risk architects and compliance engineers.
The ODC team designed a centralized governance layer around the bank’s growing AI estate rather than allowing each business unit or technical team to manage controls independently.
The first priority was visibility. Models, copilots, assistants and automated decision engines were brought into centralized inventories and registries with ownership, version history, validation status and lifecycle information.
Formal use-case intake and risk-tiering workflows were then introduced to determine which AI applications required additional review based on factors such as customer impact, data sensitivity, decision authority and the ability of human operators to override automated outcomes.
High-risk use cases were routed through defined security, legal, risk and governance checkpoints before production deployment.
The ODC model also provided ongoing monitoring and governance capacity so controls could continue to evolve as models, prompts, data sources and regulatory expectations changed.
What changed in the technology environment.
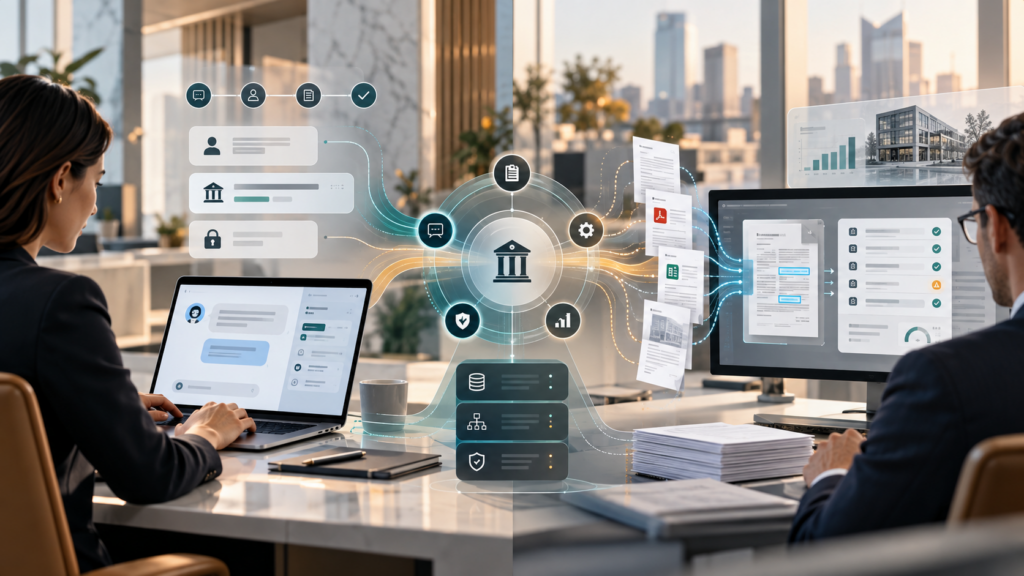
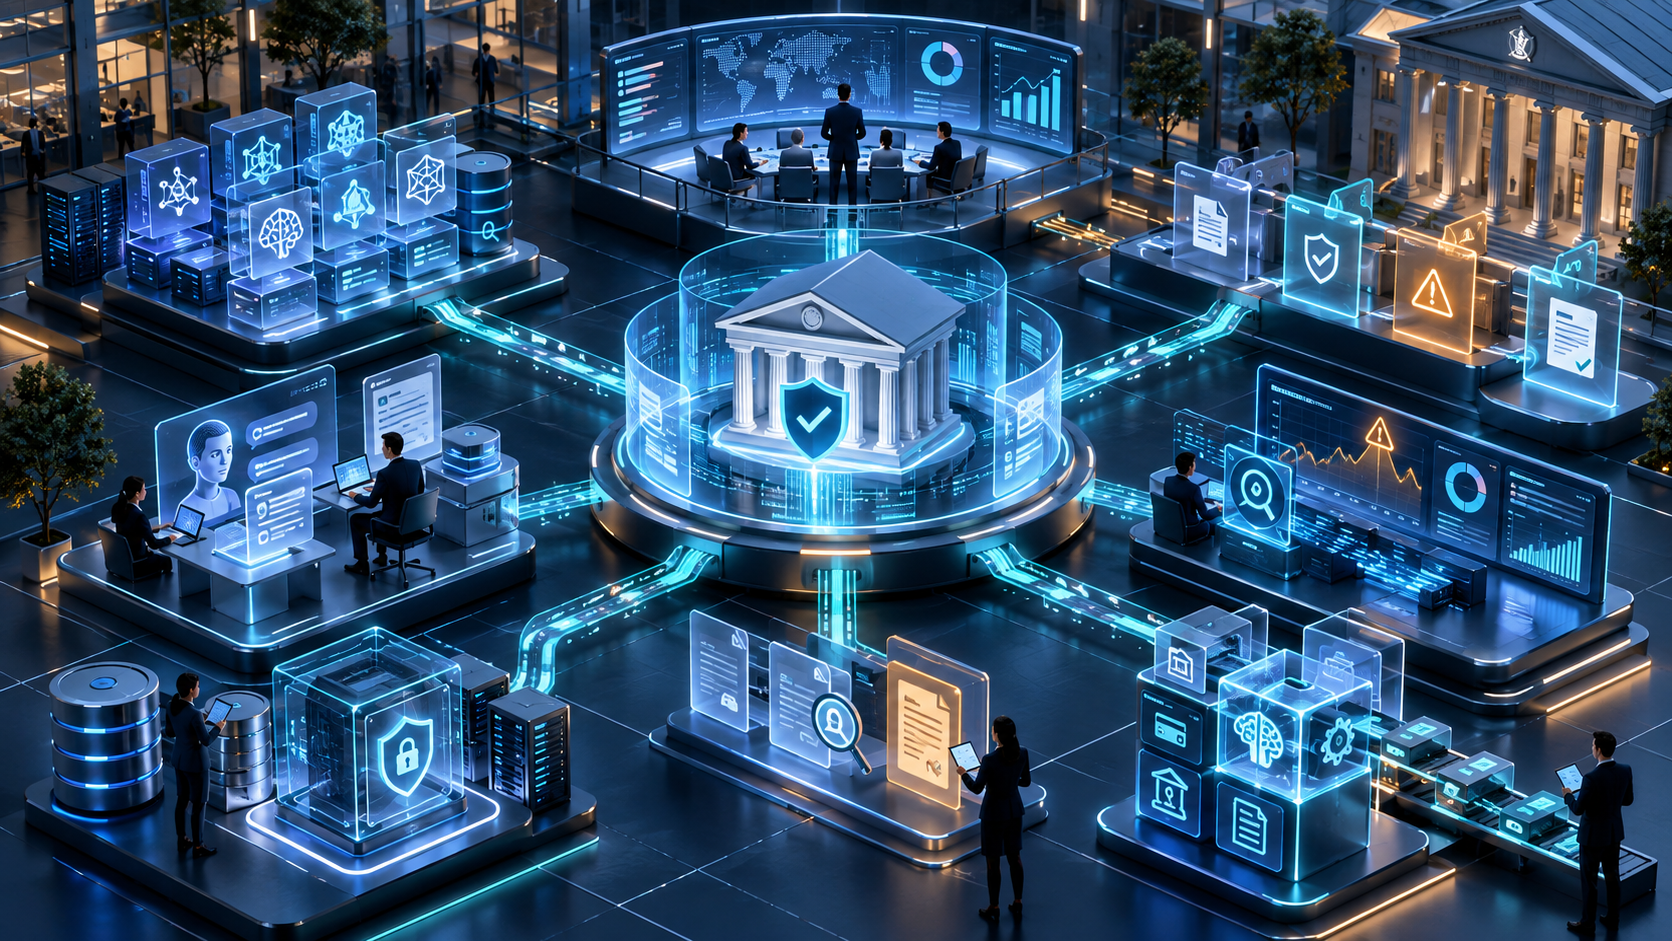
USMICRO introduced a centralized AI governance architecture spanning model inventory, approval workflows, lifecycle controls, monitoring and audit traceability.
An enterprise AI registry captured models, copilots, assistants and automated decision systems together with ownership, versions, validation results and deployment status.
Automated intake workflows classified proposed AI use cases according to customer impact, data sensitivity, decision authority and risk characteristics before routing them through the appropriate review process.
Prompt-governance and output-control layers were introduced to manage prompt behavior, output filtering, permitted tools and access boundaries.
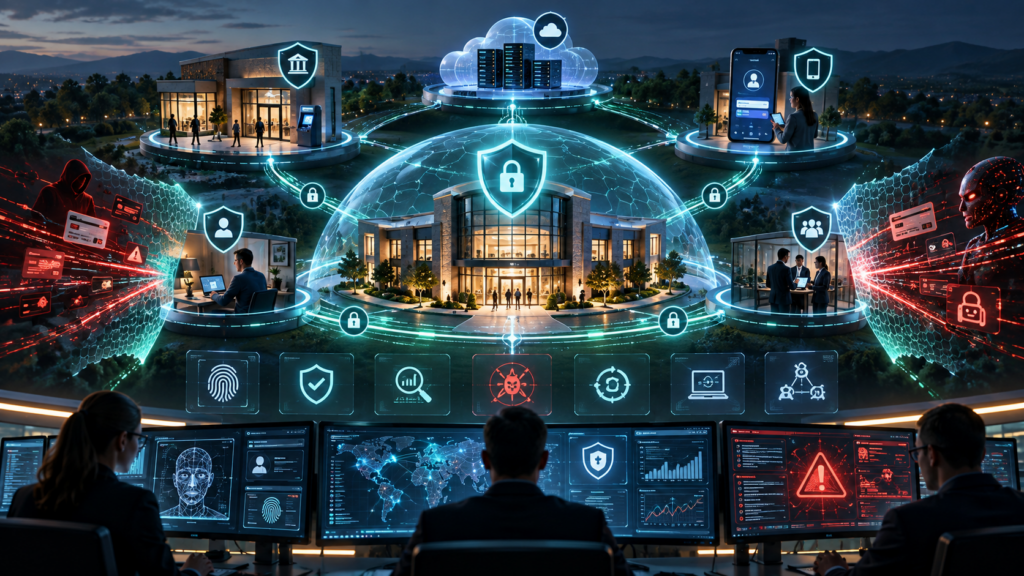
Real-time monitoring pipelines tracked indicators such as drift, anomalous behavior, potential data leakage and policy violations across deployed AI systems.
Audit-trail connectors preserved approval histories, model versions, control decisions and relevant lifecycle events so internal assurance teams and examiners could reconstruct how an AI application had been reviewed and operated.
The architectural shift was therefore from fragmented experimentation and manually governed AI use cases toward centralized inventory, risk-tiered approvals, continuous controls, lifecycle monitoring and durable decision traceability.
What can be credibly demonstrated.
The governed operating model enabled the bank to move AI initiatives toward production with stronger visibility and more consistent control across the lifecycle.
Centralized inventories eliminated blind spots around which AI systems were operating, who owned them and what validation or control status applied to each one.
Automated intake and risk-tiering workflows gave high-impact use cases a repeatable path through security, legal and governance review rather than relying on informal approval processes.
Continuous monitoring and prompt-governance controls strengthened the bank’s ability to detect emerging issues after deployment rather than treating approval as a one-time event.
Persistent audit trails improved decision traceability and made the AI environment easier to assess during internal assurance and supervisory review.
Most importantly, the bank established a reusable governance foundation that allowed AI adoption to scale with greater discipline instead of adding risk through fragmented experimentation.