Automating Governance and Compliance for a Regional Credit Union
USMICRO established an ODC-led compliance engineering model that automated recurring governance workflows, centralized policy and audit evidence, and gave the credit union a real-time view of obligations, ownership, deadlines and control status.
What needed to change.
The credit union was managing multiple regulatory, privacy, audit and internal-governance obligations with limited internal bandwidth.
Requirements associated with NCUA oversight, CFPB obligations, privacy controls, audit requests and internal policy governance were being coordinated largely through spreadsheets, email chains, manual reminders and disconnected documentation.
Teams lacked a single operational view showing which obligations were complete, overdue or awaiting approval, who owned each action, and what evidence was available to support an audit or examination.
The fragmented process increased the risk of missed deadlines, inconsistent policy execution and repeated administrative effort.
It also concentrated significant pressure around audit and examination periods, when staff had to locate, validate and assemble evidence that had accumulated across multiple systems and teams.
The underlying challenge was therefore not simply regulatory complexity. It was the absence of a continuous operating model for managing obligations, controls, documentation and evidence at scale.
How the problem was approached.
USMICRO established an Offshore Development Center model combining engineering capacity and ongoing technical operations support around the credit union’s governance and compliance environment.
Rather than treating compliance as a series of periodic manual exercises, the engineering approach focused on making recurring governance activities visible, trackable and increasingly automated.
Repetitive administrative processes — including recurring reviews, approvals, reminders, attestations, evidence collection and escalation — were converted into structured workflows.
The ODC team also centralized compliance obligations and supporting documentation so that internal credit-union staff could spend more time on interpretation, judgment and oversight rather than administrative coordination.
Development and support were delivered iteratively through the extended ODC model, allowing workflows, dashboards and controls to evolve as regulatory requirements and internal governance needs changed.
What changed in the technology environment.
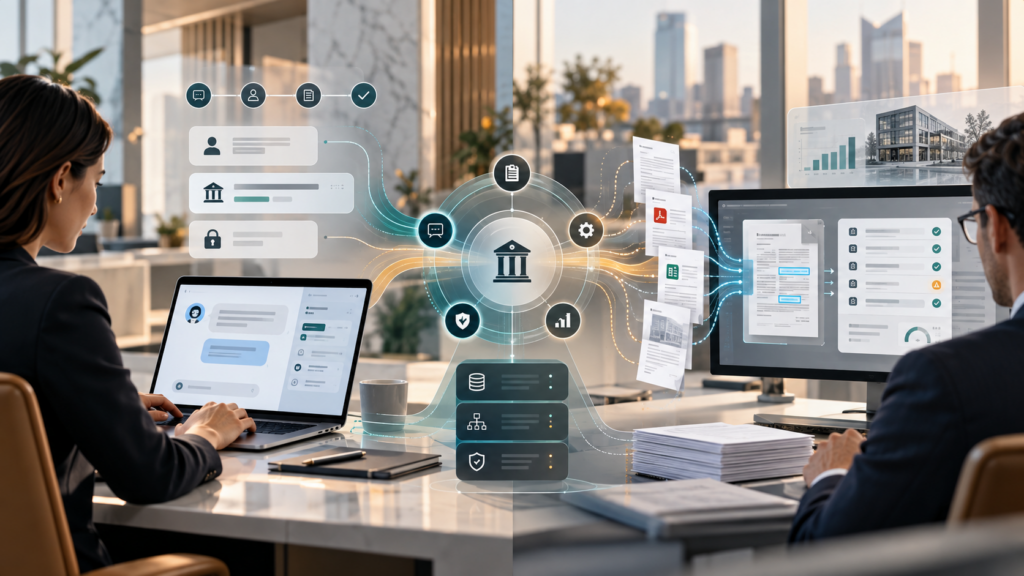
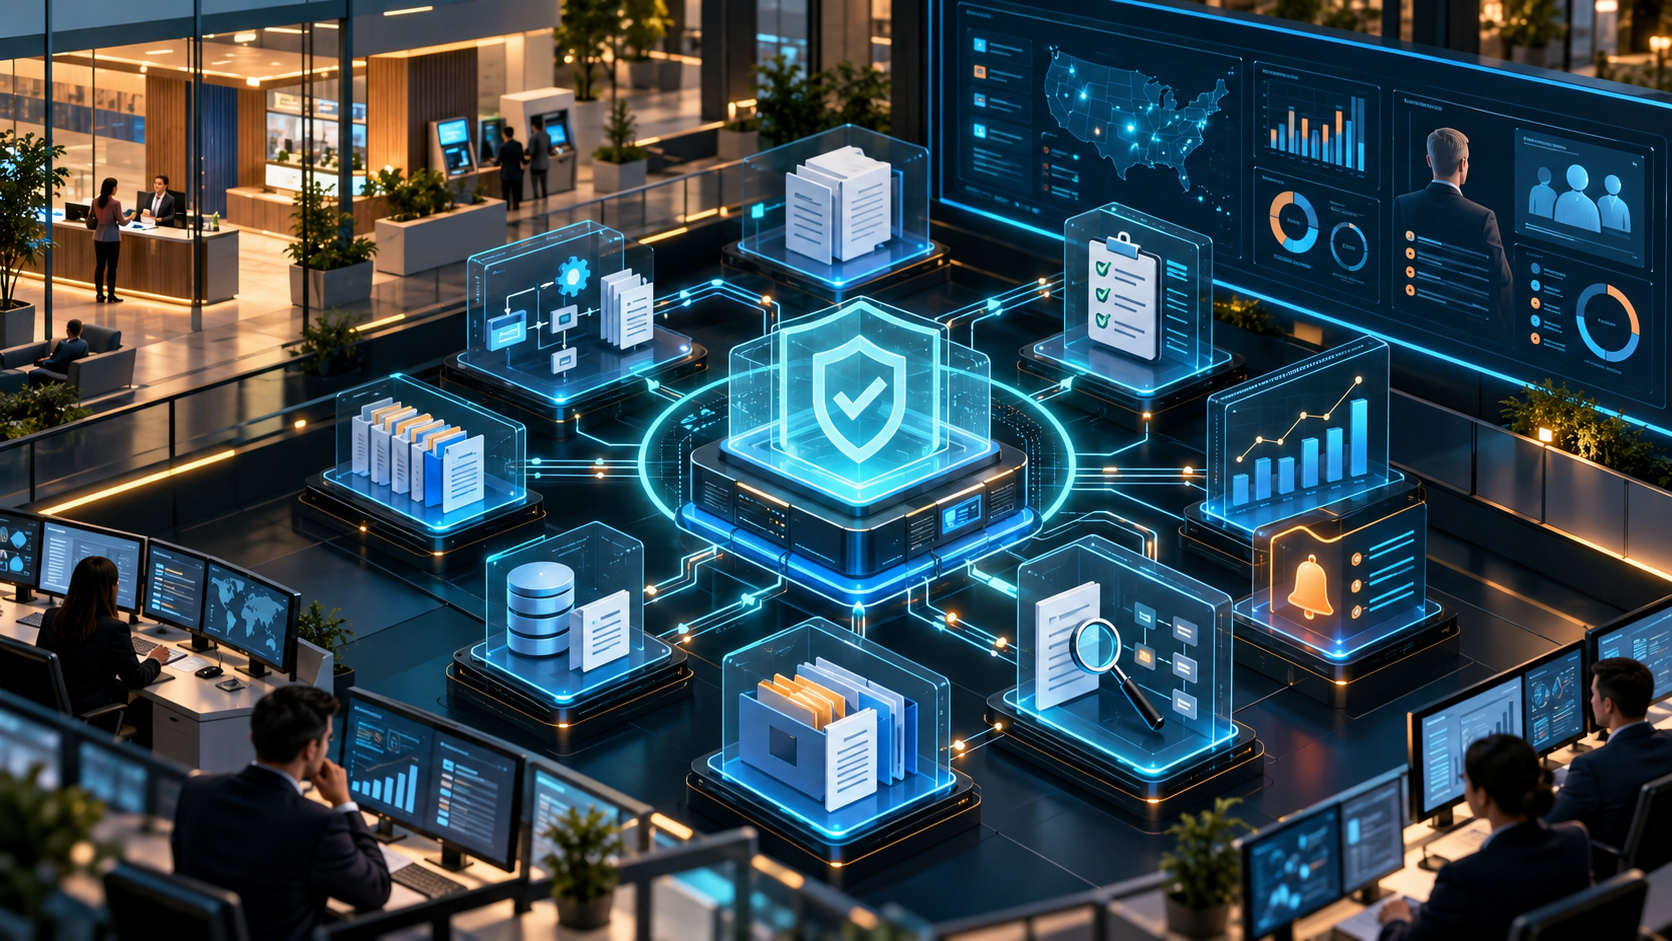
USMICRO introduced a centralized governance and compliance environment connecting workflow automation, policy management, evidence tracking, dashboards and audit-support processes.
Automated workflow engines managed recurring reviews, approvals, mandatory actions and role-based escalations, replacing manual reminders and email-driven coordination.
Real-time compliance dashboards provided visibility into obligation status, control ownership, risk indicators, upcoming deadlines and overdue actions.
Policy and control-management components introduced structured document versioning, staff attestations and approval histories so that organizations could demonstrate which policy version was active, who had acknowledged it and when required reviews had occurred.
Evidence-mapping mechanisms linked regulatory obligations and internal controls to the documentation and audit trails needed to demonstrate execution.
Automated reporting and audit-trail connectors reduced the need to repeatedly assemble the same information for examinations and internal reviews.
The architectural shift was therefore from distributed spreadsheets, email reminders and manually assembled evidence toward centralized workflows, governed documentation, continuous control visibility and reusable audit evidence.
What can be credibly demonstrated.
The new governance environment materially reduced the administrative burden associated with recurring compliance and audit-preparation activities.
Automating document requests, reminders, approvals and recurring control activities reduced the amount of manual coordination required from internal teams.
Centralized documentation and persistent audit trails also shortened the effort required to assemble and validate regulatory examination packages.
Policy attestation and review workflows became significantly more consistent because ownership, deadlines and completion status could be monitored through a single operating environment.
The ODC model gave the credit union continuing engineering and technical operations capacity without requiring the institution to build an equivalent internal team for every compliance-system requirement.
Beyond the immediate efficiency gains, leadership gained a more scalable governance foundation with clearer accountability, stronger evidence discipline and better visibility into compliance execution.